October 4, 2021, has all the chances to become a BGP awareness day.
Memes aside, yesterday, with the entirety of its ecosystem including vast resources like Instagram and WhatsApp, Facebook disappeared from the Internet.

October 4, 2021, has all the chances to become a BGP awareness day.
Memes aside, yesterday, with the entirety of its ecosystem including vast resources like Instagram and WhatsApp, Facebook disappeared from the Internet.
Since 2014 Qrator Labs has developed a BGP monitoring and analytics service called Qrator.Radar. One of its main features is monitoring specific BGP anomalies that could result in an incident that we would further call either a BGP route leak or BGP hijack.
Both of them reroute traffic to third parties, compared to the no-anomaly state, but differently. Over the last few years, a lot of efforts have been invested in solving those issues, but there are still misunderstandings about what is what and how different tools are helping resolve different problems.
Yesterday, on February 19 Internet observed yet another demonstration of a handy Noction feature that is probably supposed to get you rich but is more likely to make you infamous.
Starting from 09:48 UTC, we saw around 200 thousand routes of previously non-existent prefixes with broken AS_PATH. But first things first.
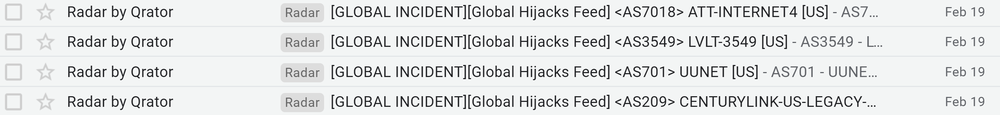
The day started with a rather harsh and buzzing sound of email notifications for critical routing events, which, as you can see, are cut off on such a high threshold that we consider those to be global.
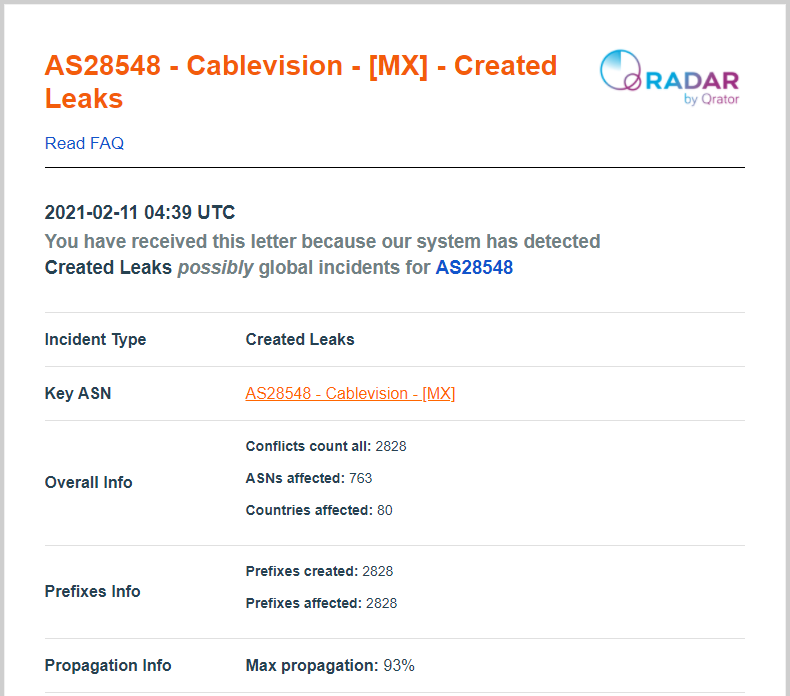
February 11, 2021 - AS28548 - Cablevision - leaked 2828 prefixes, creating 2828 conflicts for 763 ASNs in 80 countries. Maximum propagation: 93%. Severity: High.
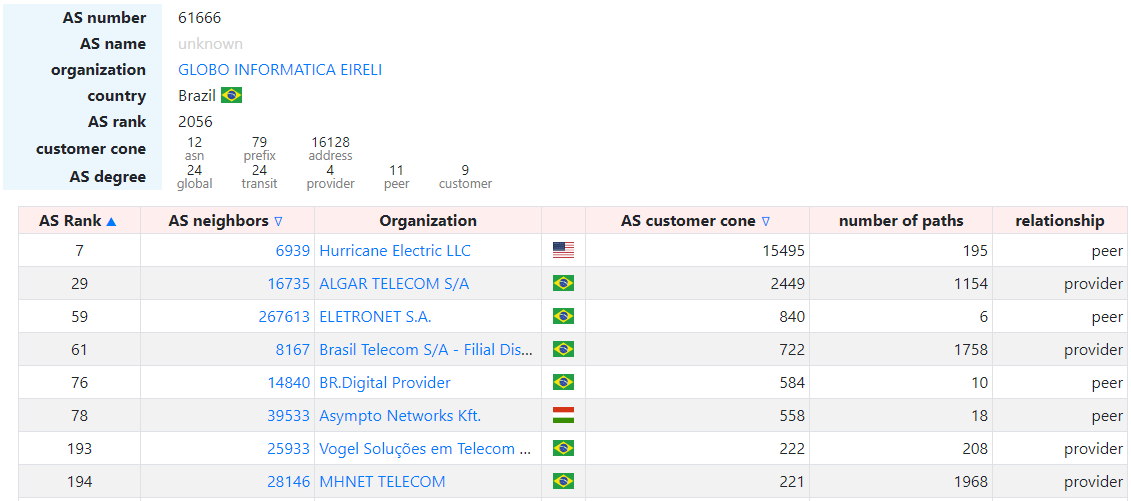
January 27 of the year 2021 was marked with quite a peculiar route leak. AS61666 - GLOBO started announcing prefixes of its upstream provider MHNET - AS28146 to its another provider ALGAR - AS16735. In three minutes GLOBO leaked 1330 prefixes, and the whole routing incident lasted for 8 minutes - a time that was enough to create 1435 conflicts in 21 countries with 265 ASNs, mainly in Brazil (194 ASNs), United States (22 ASNs) and Venezuela (7 ASNs).
One would expect 2021 to start somewhat differently compared with chaos of the previous year. In Qrator.Radar, we also hoped for the better. Unfortunately, as soon as January 6 - today, we proved wrong.
AS203, belonging to what was formerly known as "Level3", acquired by "CenturyLink" in 2016, latter rebranded as "Lumen" in 2020, is a frequent visitor within the incident reports of the Qrator.Radar team. We are not here to blame anyone, but such occurrence of routing incidents for a single organization is worrying - we hope this article would help you to understand how even a small event could reach enormous impact with specific prerequisites met.
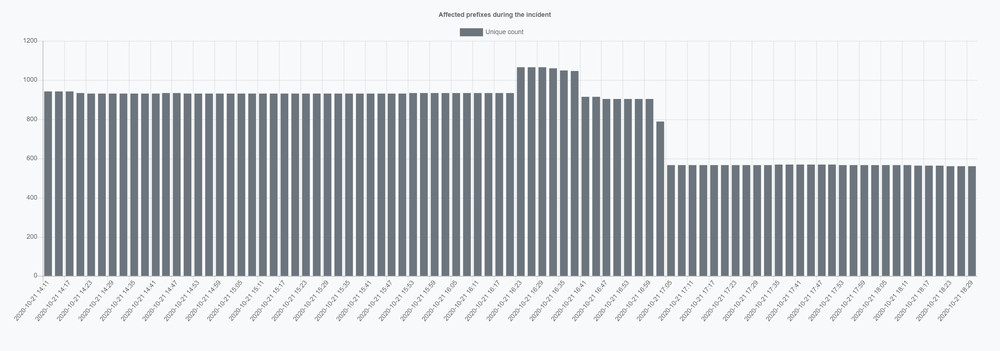
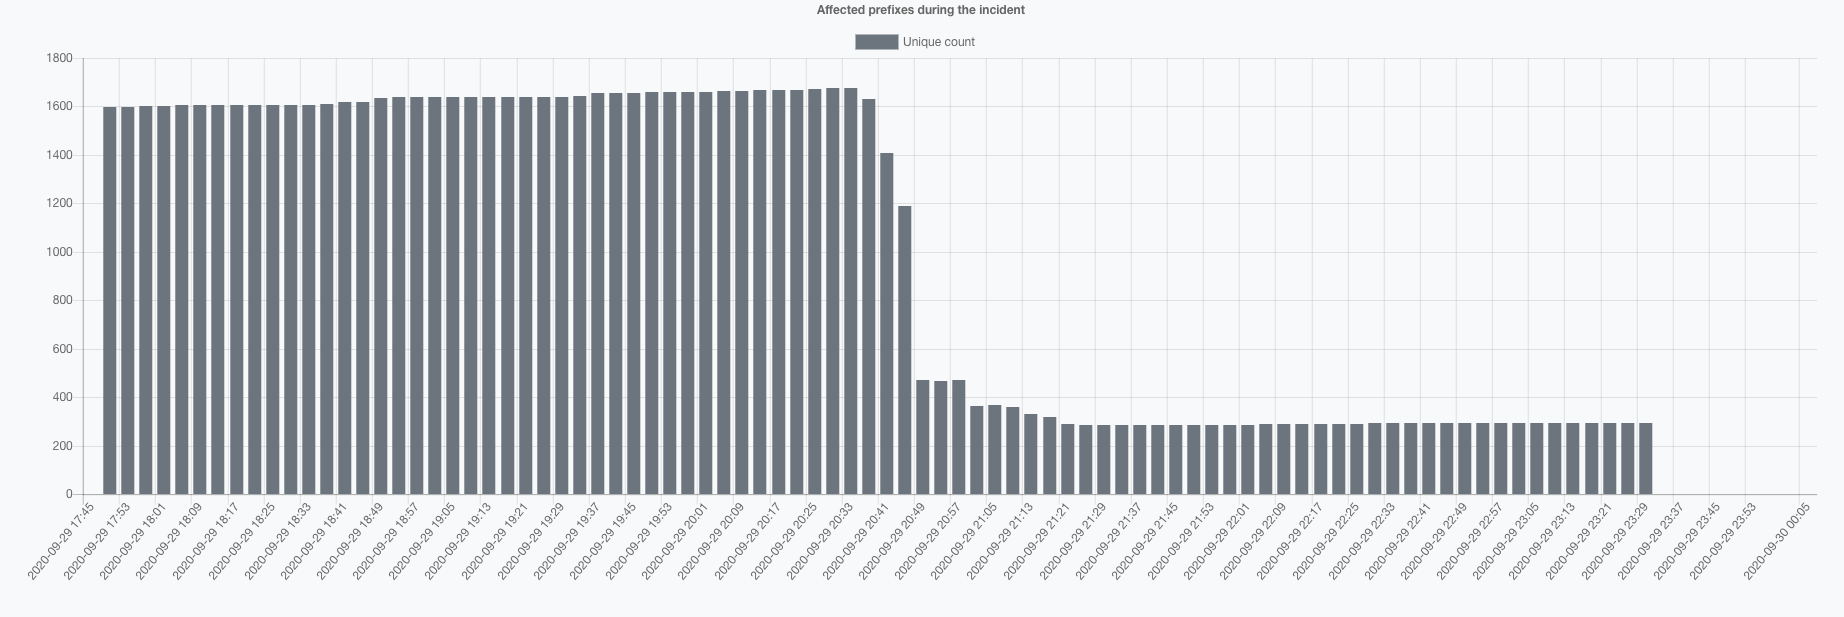
On Tuesday, September 29, 2020 AS1221 - Telstra announced 472 prefixes in a BGP hijack event that affected 266 other ASNs in 50 countries, with the most damage rendered to the U.S. and U.K. based networks. Worldwide it affected more than 1680 IPv4 prefixes, creating almost 2000 path challenge conflicts.
On Sunday, August 30, 2020, it all started with a simple question: “What’s happening?”
Approximately around 10 UTC, the global Internet started experiencing a very specific state of connectivity - inside the network of one of the largest Tier-1 operators in the world, CenturyLink (primary AS3356), something bad was undoubtedly going on.
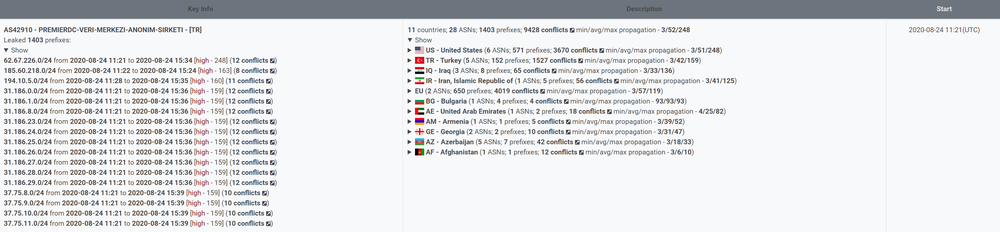
Yesterday, on August 24, 2020, Qrator.Radar BGP monitoring saw a rather large route leak originating from the AS42910 - Premier DC, containing 1403 prefixes mainly from the United States (571) and, peculiarly, Akamai. And then almost all the Western Asia region countries.